

Meet Josys AI: AI-Native Identity Security and Governance at Enterprise Scale
Join hundreds of companies and start your identity governance journey today
Josys AI is our AI suite for identity security and governance - built into the platform rather than bolted on top. It reads your identity and usage data as it changes and offers the next step: drafting an access policy, flagging an unknown AI tool, classifying a service account. That's what we mean by AI-native identity security - the intelligence sits inside the workflow you were already in, rather than in a report you read afterwards.
Here are a few of the AI-powered features now on the Josys platform:
AI-Powered Policy Generation & Drift Detection
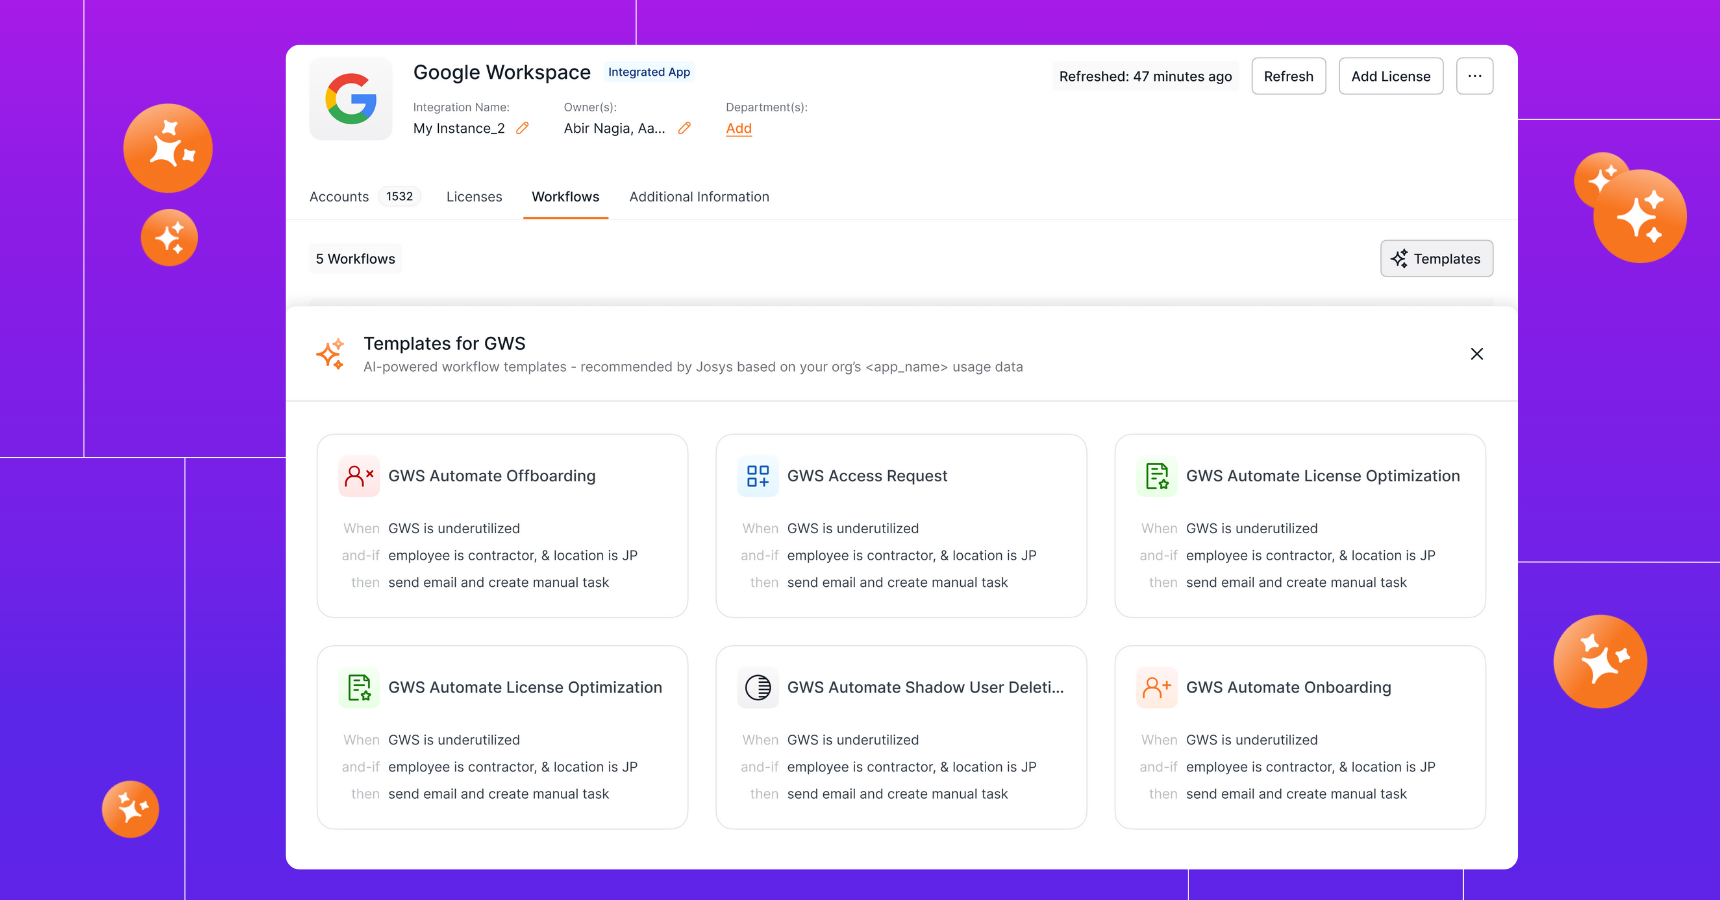
Managing access policies manually is time-consuming, error-prone, and often leads to over-permissioned users or outdated controls. As organizations grow and SaaS adoption scales, IT teams struggle to keep policies aligned with actual usage and business roles. This misalignment creates security risks, compliance gaps, and unnecessary administrative overhead.
Our new AI-Powered Policy Generation & Drift Detection feature solves this by automatically analyzing identity data and usage patterns to recommend and create precise access policies by role and department. It continuously monitors for policy drift—unauthorized changes or deviations—and either flags them for review or triggers exception workflows to restore compliance quickly. This gives IT teams real-time visibility and control over access governance, dramatically reducing manual effort while strengthening security posture.
Shadow AI Discovery
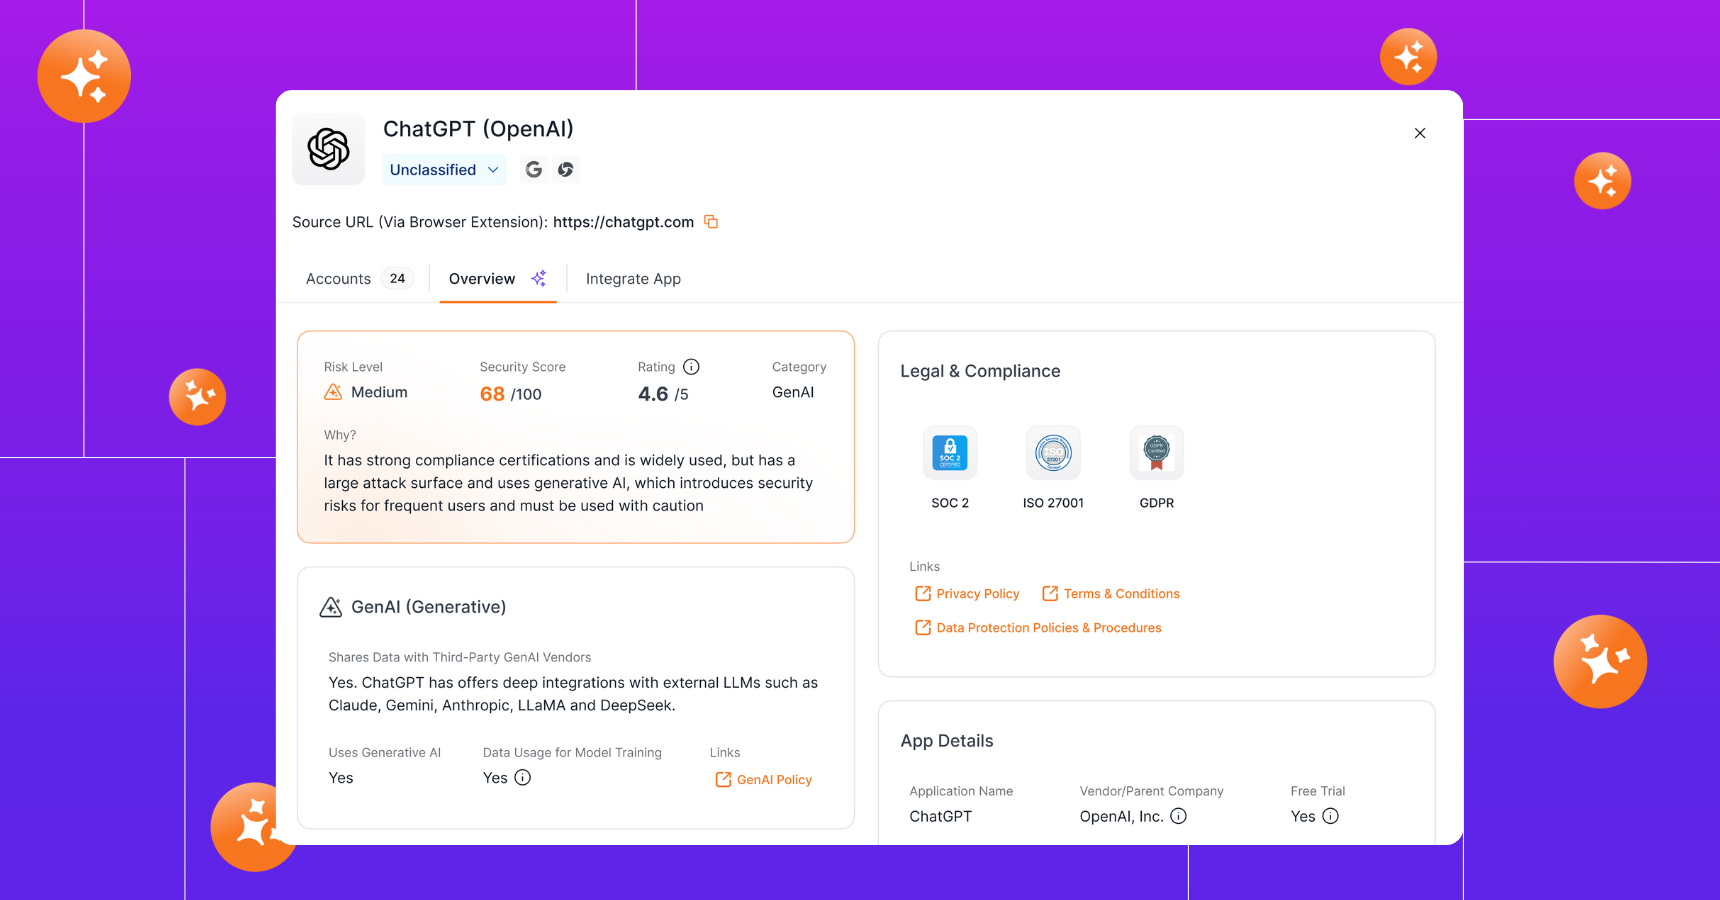
The rapid rise of AI tools has led to a surge in unsanctioned or unvetted applications being used across organizations—often without IT's knowledge. This “Shadow AI” introduces significant security, compliance, and data privacy risks, as teams experiment with tools that may lack proper controls or oversight. Without visibility, IT can't assess risk, enforce policies, or ensure safe AI adoption across departments.
Our new Shadow AI Discovery and Risk Analyzer feature brings these blind spots into focus by automatically detecting AI tools in use throughout your environment. It evaluates each app's risk profile using public data, open-source intelligence, and vendor-specific insights—helping IT teams quickly identify which tools require review, restriction, or approval. With this visibility, organizations can proactively manage AI risk and ensure safe, compliant use of emerging technologies.
Automated Identity Classification
As organizations scale, managing a growing number of human and non-human identities—like service accounts, bots, and automation tools—becomes increasingly complex. These accounts often go unmonitored, misconfigured, or duplicated, creating blind spots and increasing the risk of unauthorized access or credential misuse. Without clarity on which identities are valid and what access they truly need, IT teams struggle to enforce proper controls and respond to threats effectively.
Our new Identity Classification and Access Recommendation feature automatically detects and tags both human and non-human identities, assigning confidence scores to help IT assess their legitimacy. It enables teams to accept or reject recommendations and apply the right access permissions, reducing overprovisioning and ensuring stronger identity hygiene. This also streamlines investigations by highlighting duplicate or suspicious identities, allowing IT to focus on what matters most.

Contract Enrichment for Cost Optimization
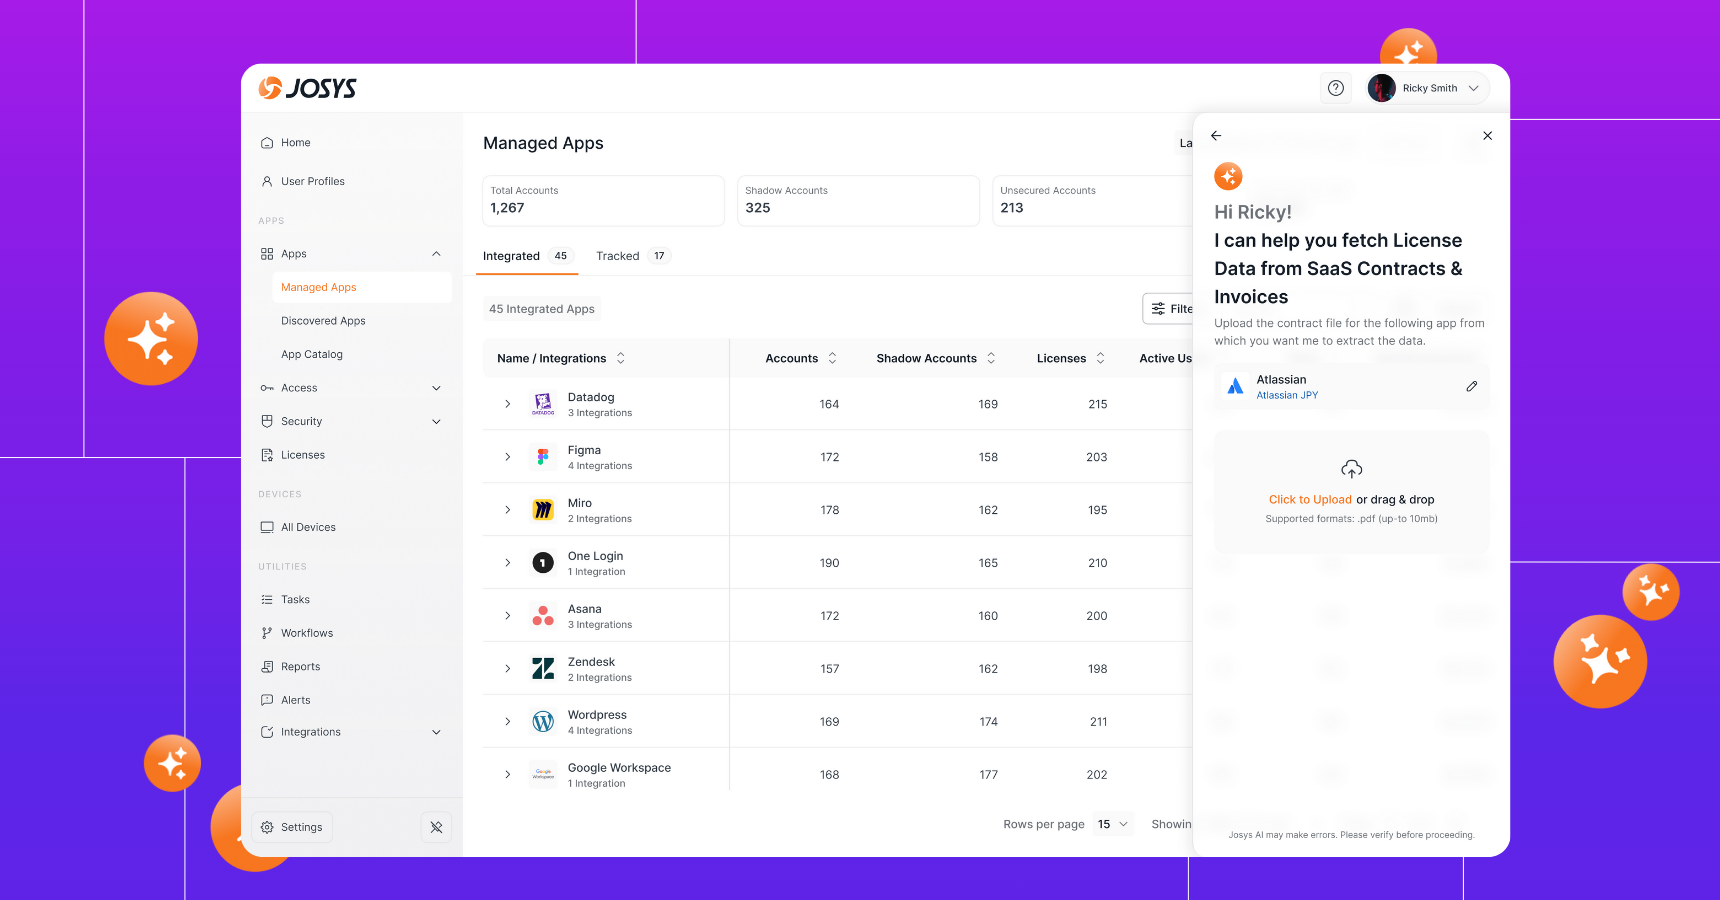
Tracking SaaS contracts manually is tedious and error-prone, often leading to missed renewals, unused licenses, or unfavorable terms slipping through the cracks. Without centralized visibility into contract details, IT and procurement teams struggle to optimize costs or negotiate effectively.
Our new Contract Enrichment for Cost Optimization feature automatically parses uploaded SaaS contracts to extract renewal dates, license counts, and key terms. This information is integrated directly into each app's profile, with proactive alerts that help teams stay ahead of renewals and cut unnecessary spend.
Responsible & Contextual AI
- Embedded into Josys' privacy-first infrastructure: AI tools appear contextually where and when they're needed.
- Committed to enterprise-grade AI: transparent models, vendor oversight, and no training on customer data without explicit permission.
For the wider picture - how to govern AI tools and agents across your whole organization, and what to measure - see our guide to enterprise AI governance.
The Josys AI Transformation
Josys AI transforms IT operations by:
- Reducing manual work: Automates tedious governance and identity tasks.
- Strengthening security posture: Continuous monitoring of access and AI usage risks.
- Optimizing cloud spend: Proactive license and contract management.
- Boosting IT agility: Intelligent automation that incorporates IT oversight.
Looking Ahead
Josys plans to expand autonomous support with more ITSM agent features in future updates, further streamlining help desk efficiency and SaaS lifecycle control. Want to see it in action? Request a demo and explore how Josys AI can power up your SaaS strategy.
FAQs
What's the difference between AI-native and AI-powered identity security?
AI-powered usually means AI was added to an existing product - it can summarize activity or generate a report after the fact. AI-native means the intelligence is part of the platform itself, reading identity and usage data as it changes and offering the next action inside the workflow rather than in a separate tool.
Does Josys train AI models on customer data?
No, not without explicit permission. Josys AI uses transparent models with vendor oversight, and customer data is not used for training unless a customer specifically opts in.
Does Josys AI make changes on its own, or does IT approve them?
IT stays in control. Josys AI produces recommendations - access policies, identity classifications, risk flags - and your team accepts or rejects them. Automation runs where you've allowed it, not by default.
Does Josys AI cover non-human identities?
Yes. Identity classification detects and tags both human and non-human identities, including service accounts, bots and automation tools, and assigns each a confidence score so IT can judge whether it's legitimate and what access it should have.
Which Josys AI features are available now?
Policy generation and drift detection, Shadow AI discovery and risk analysis, automated identity classification with access recommendations, and contract enrichment for cost optimization. Autonomous ticket resolution is on the roadmap.
over your identities, applications, and files?
Sign-up for a 14-day free trial and transform your IT operations.




Questions? Answers.

What is Josys?

End-to-End Identity
Governance made easy for IT


