

Access requests are where
governance breaks down.
Manual access request management slows down governance and leaves security teams unable to see who has access to what.

Scattered requests
Asks arrive through Slack, email and tickets, with no single place to track them.

Stalled approvals
MFA gaps, excess admin rights & orphaned accounts hide inside app-by-app reports

Ungoverned access
Access granted outside policy leaves no audit trail and more risk.
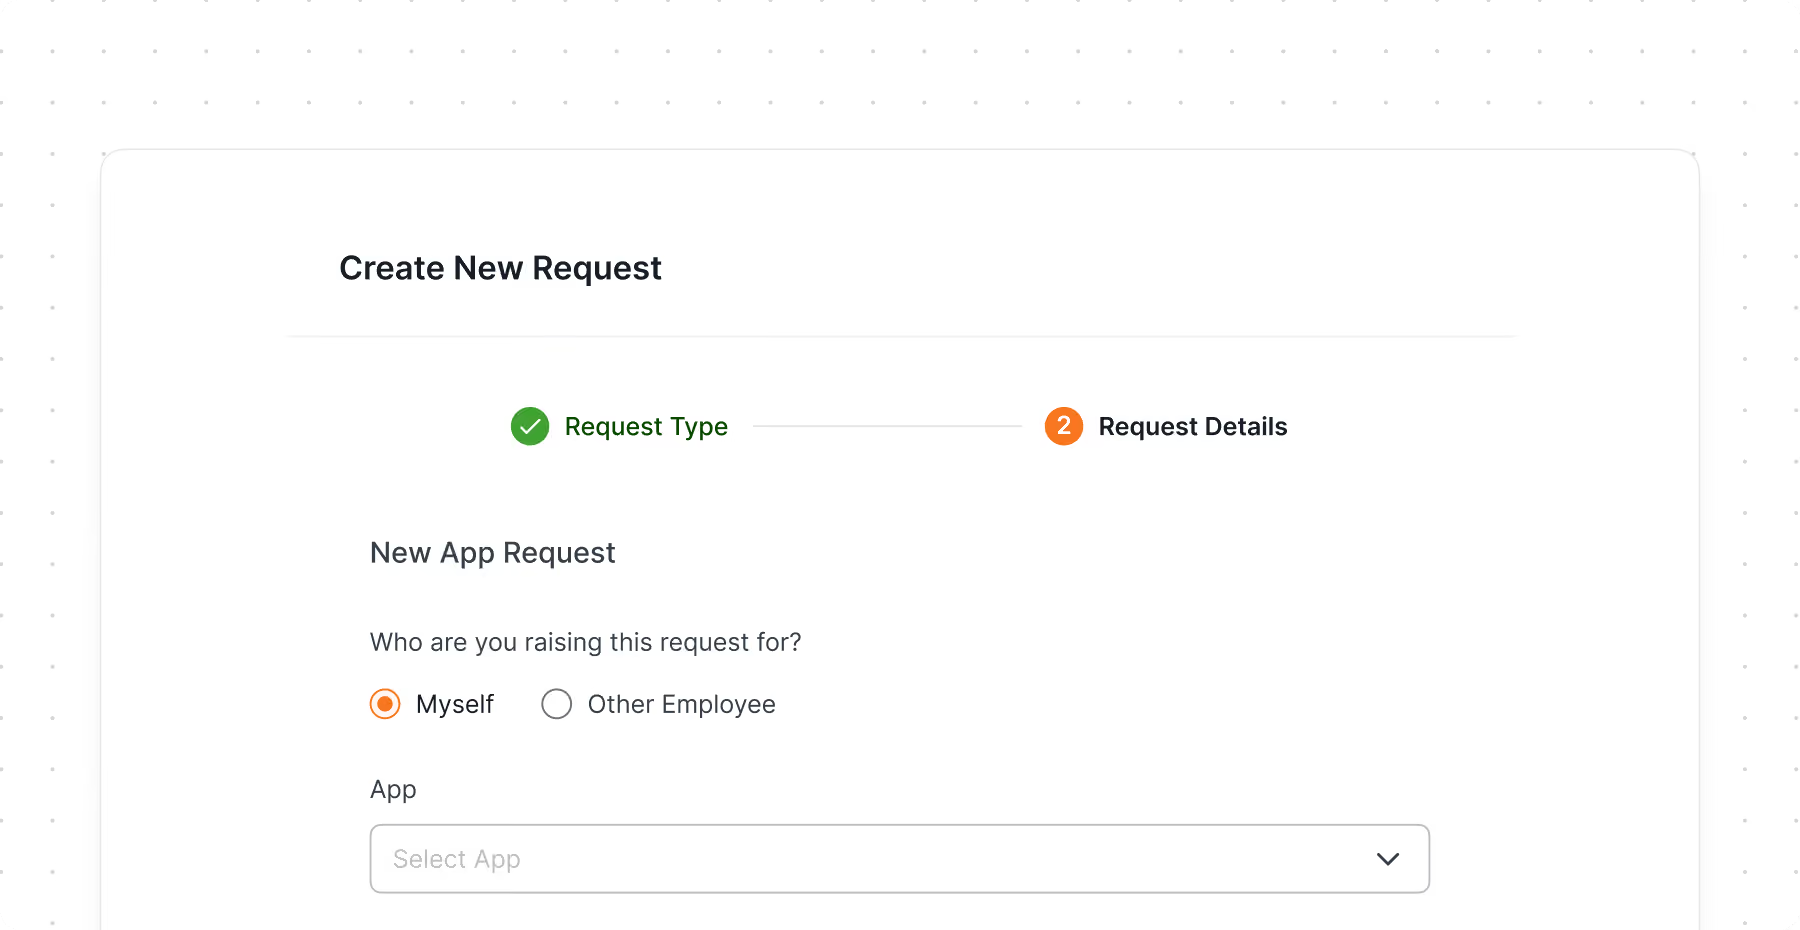
Approvals that run on policy, not follow-ups.
Set the rules once. Every request from the portal is routed to the right approver, checked against policy, and provisioned automatically once approved, with a full audit trail behind it.
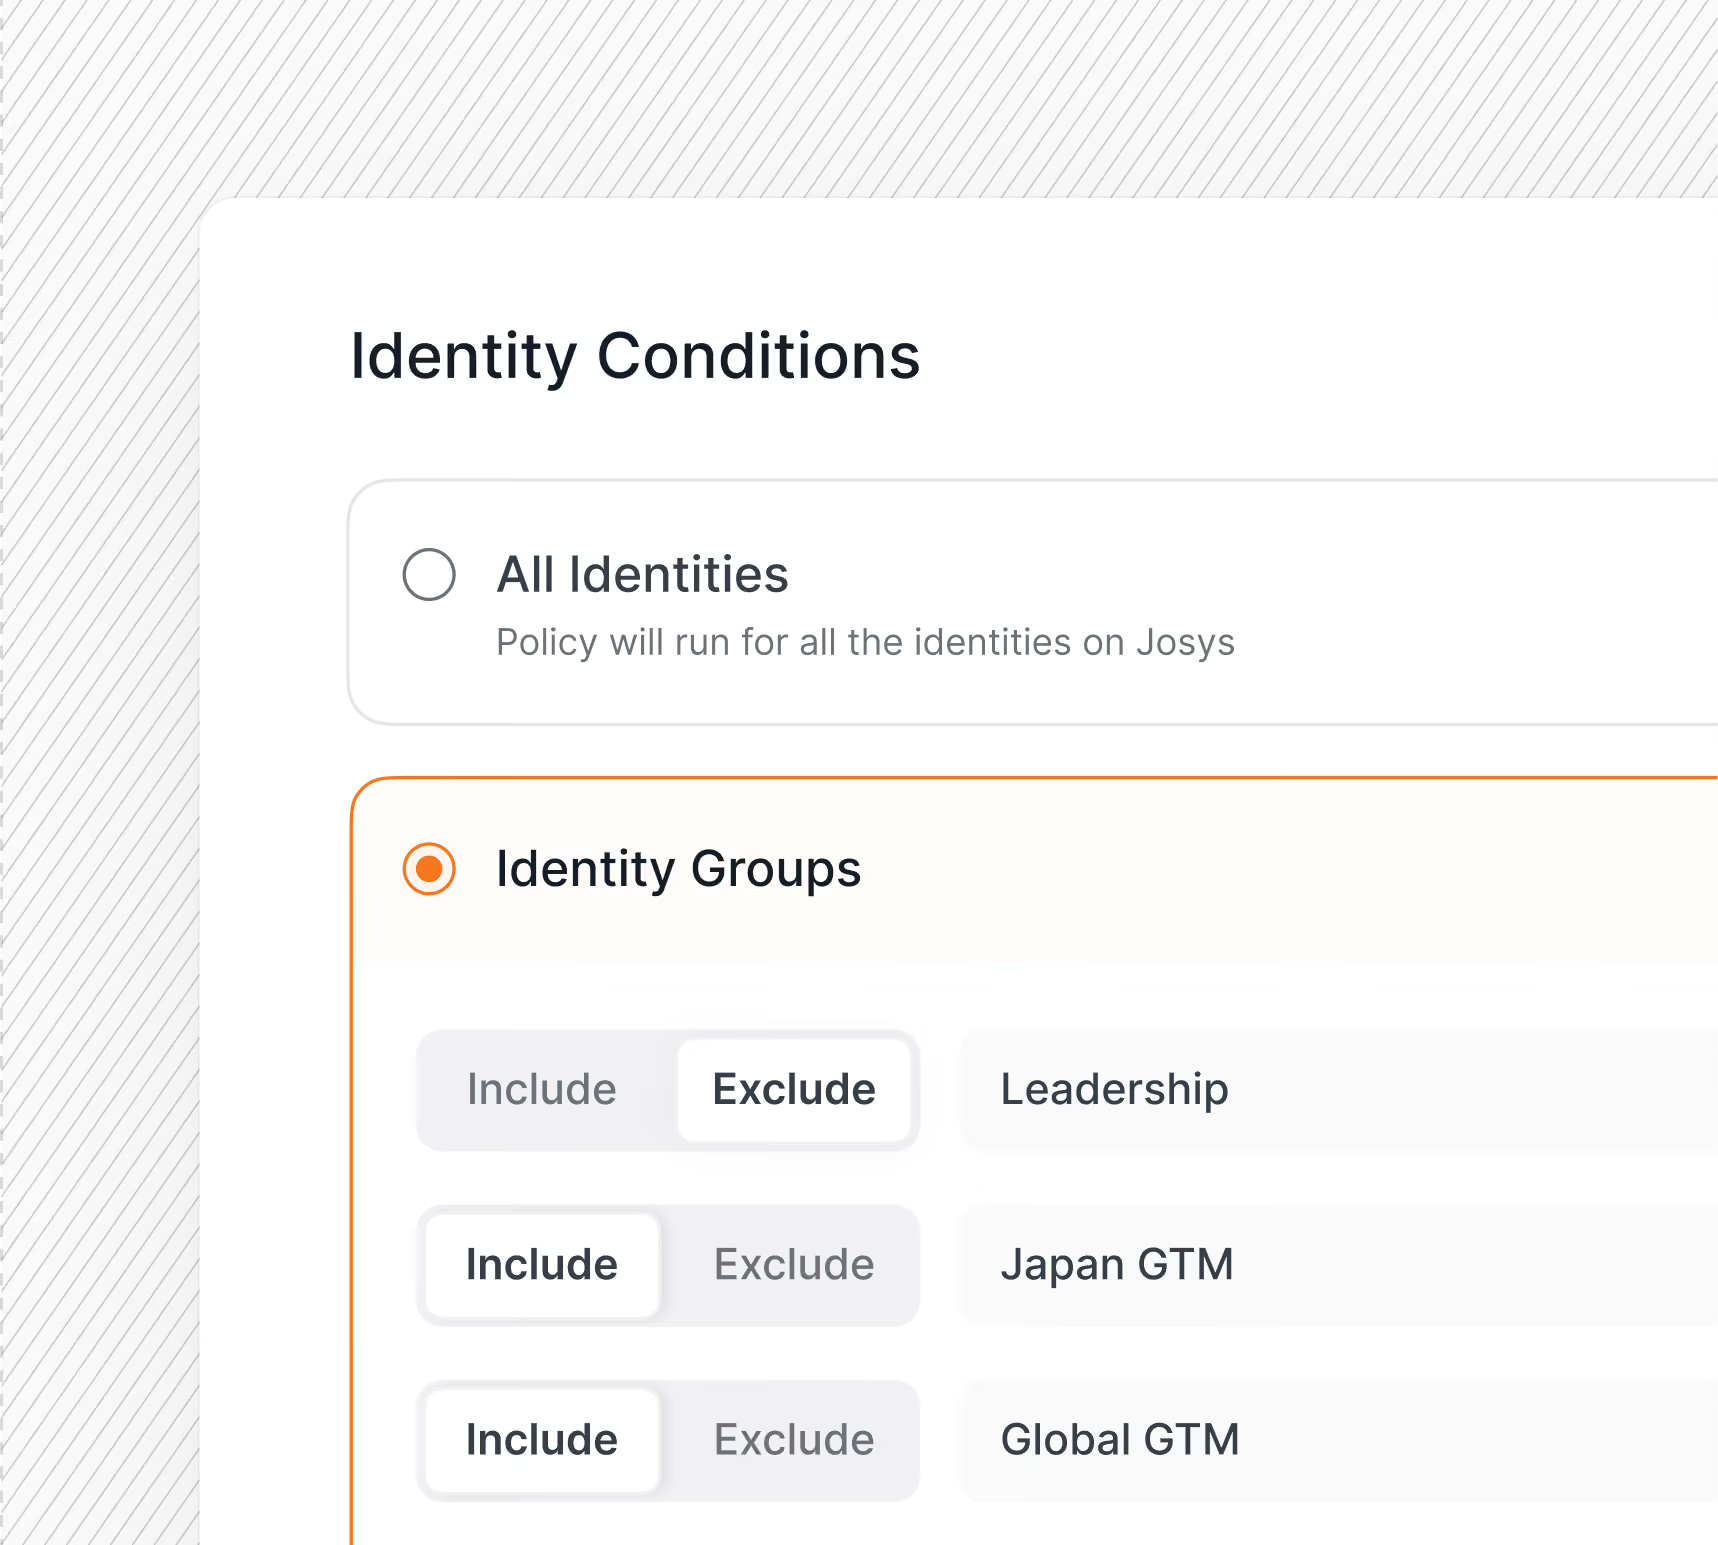
Apply each policy to all identities, specific identity groups, or based on other custom parameters, then choose the apps it covers.
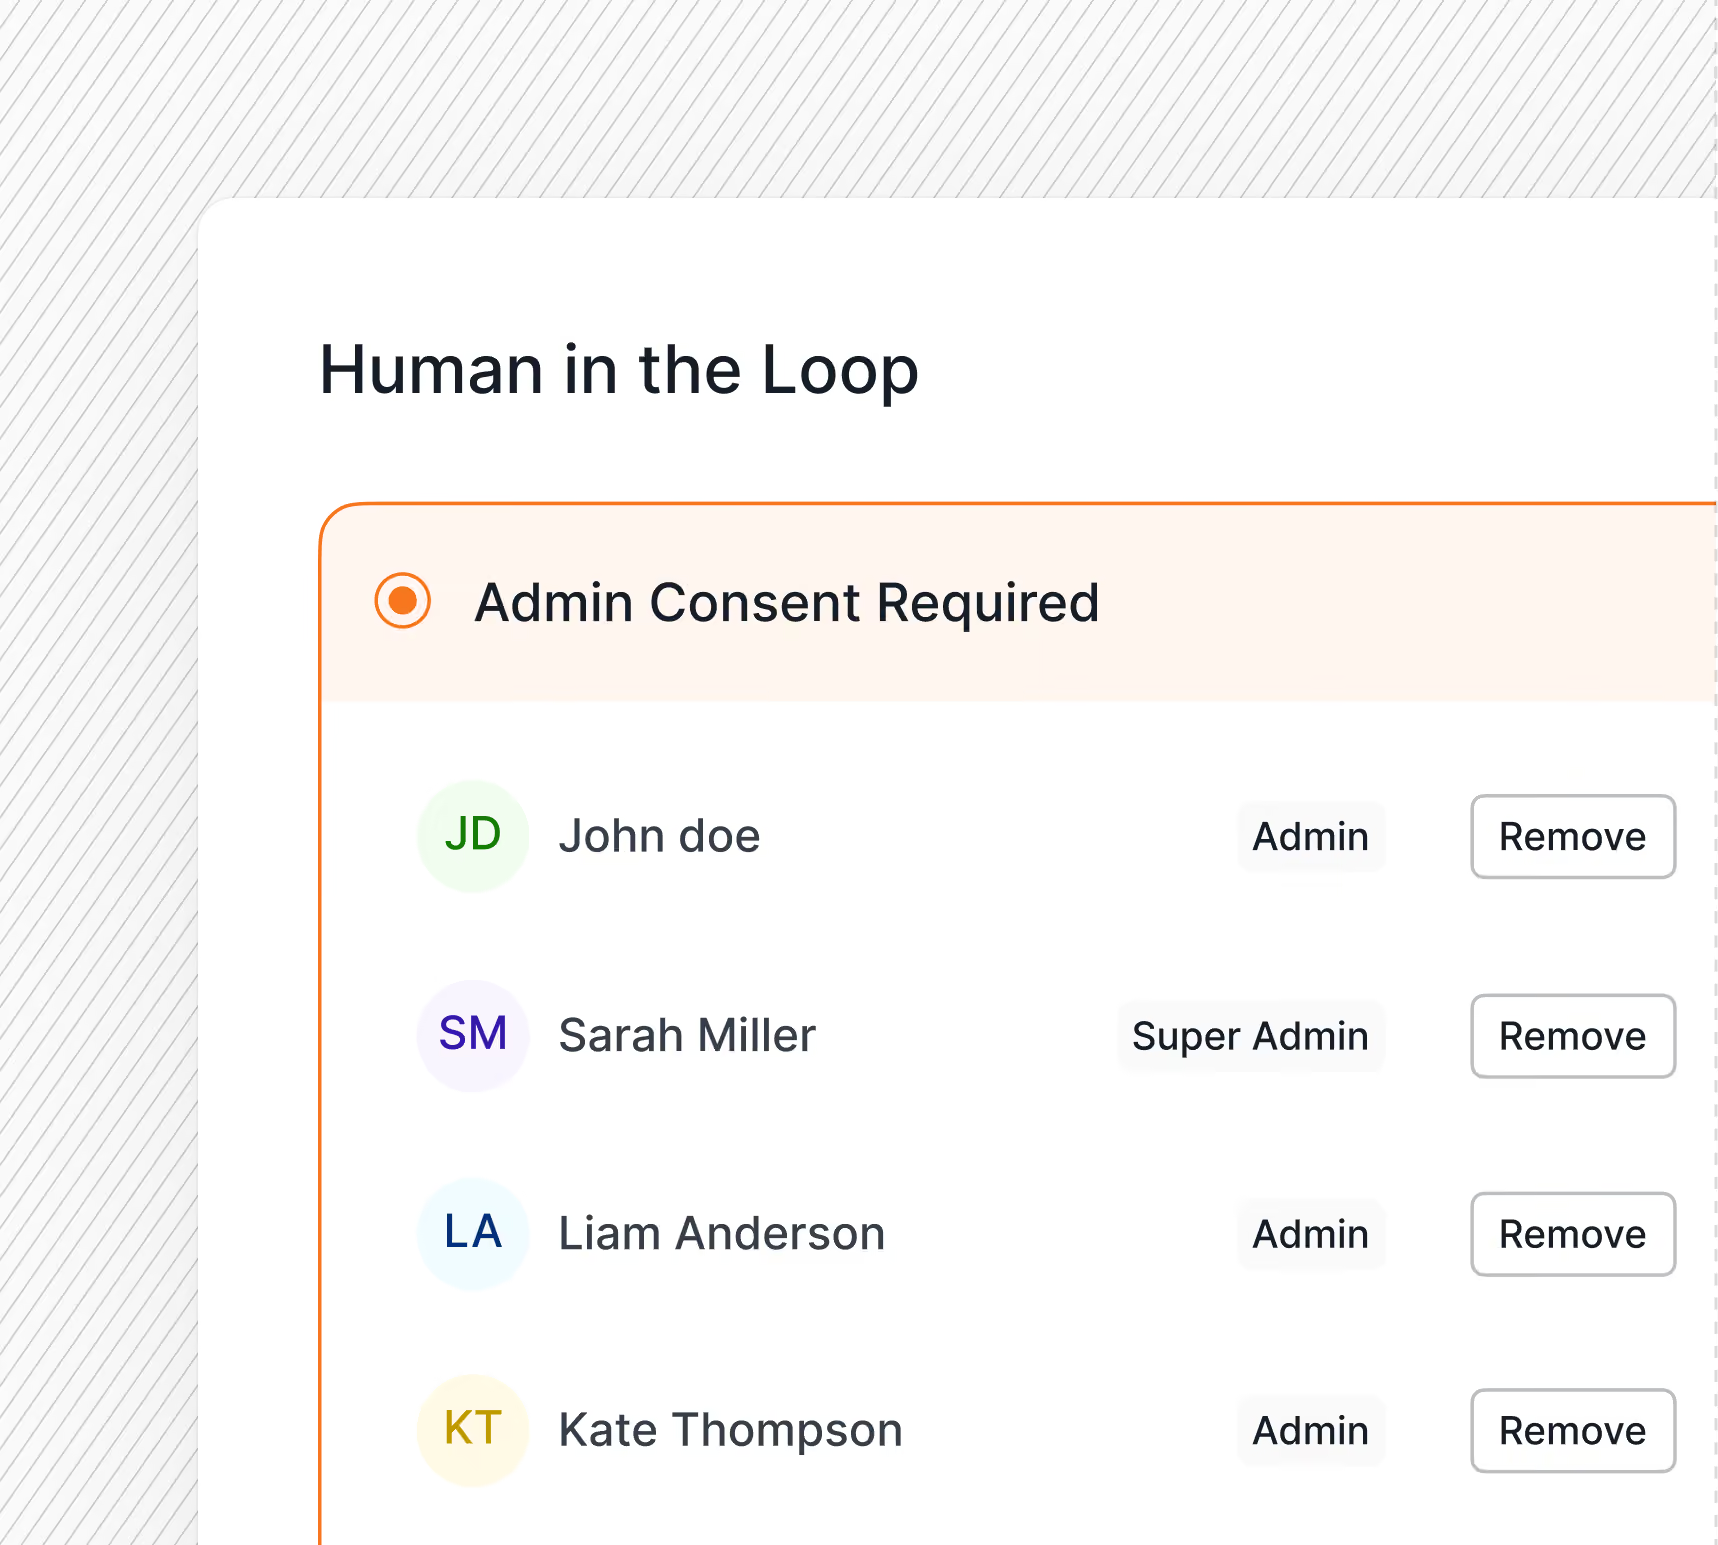
Assign app owners, managers, or IT as approvers, so every request reaches the right person and never stalls in a queue.
automated actions
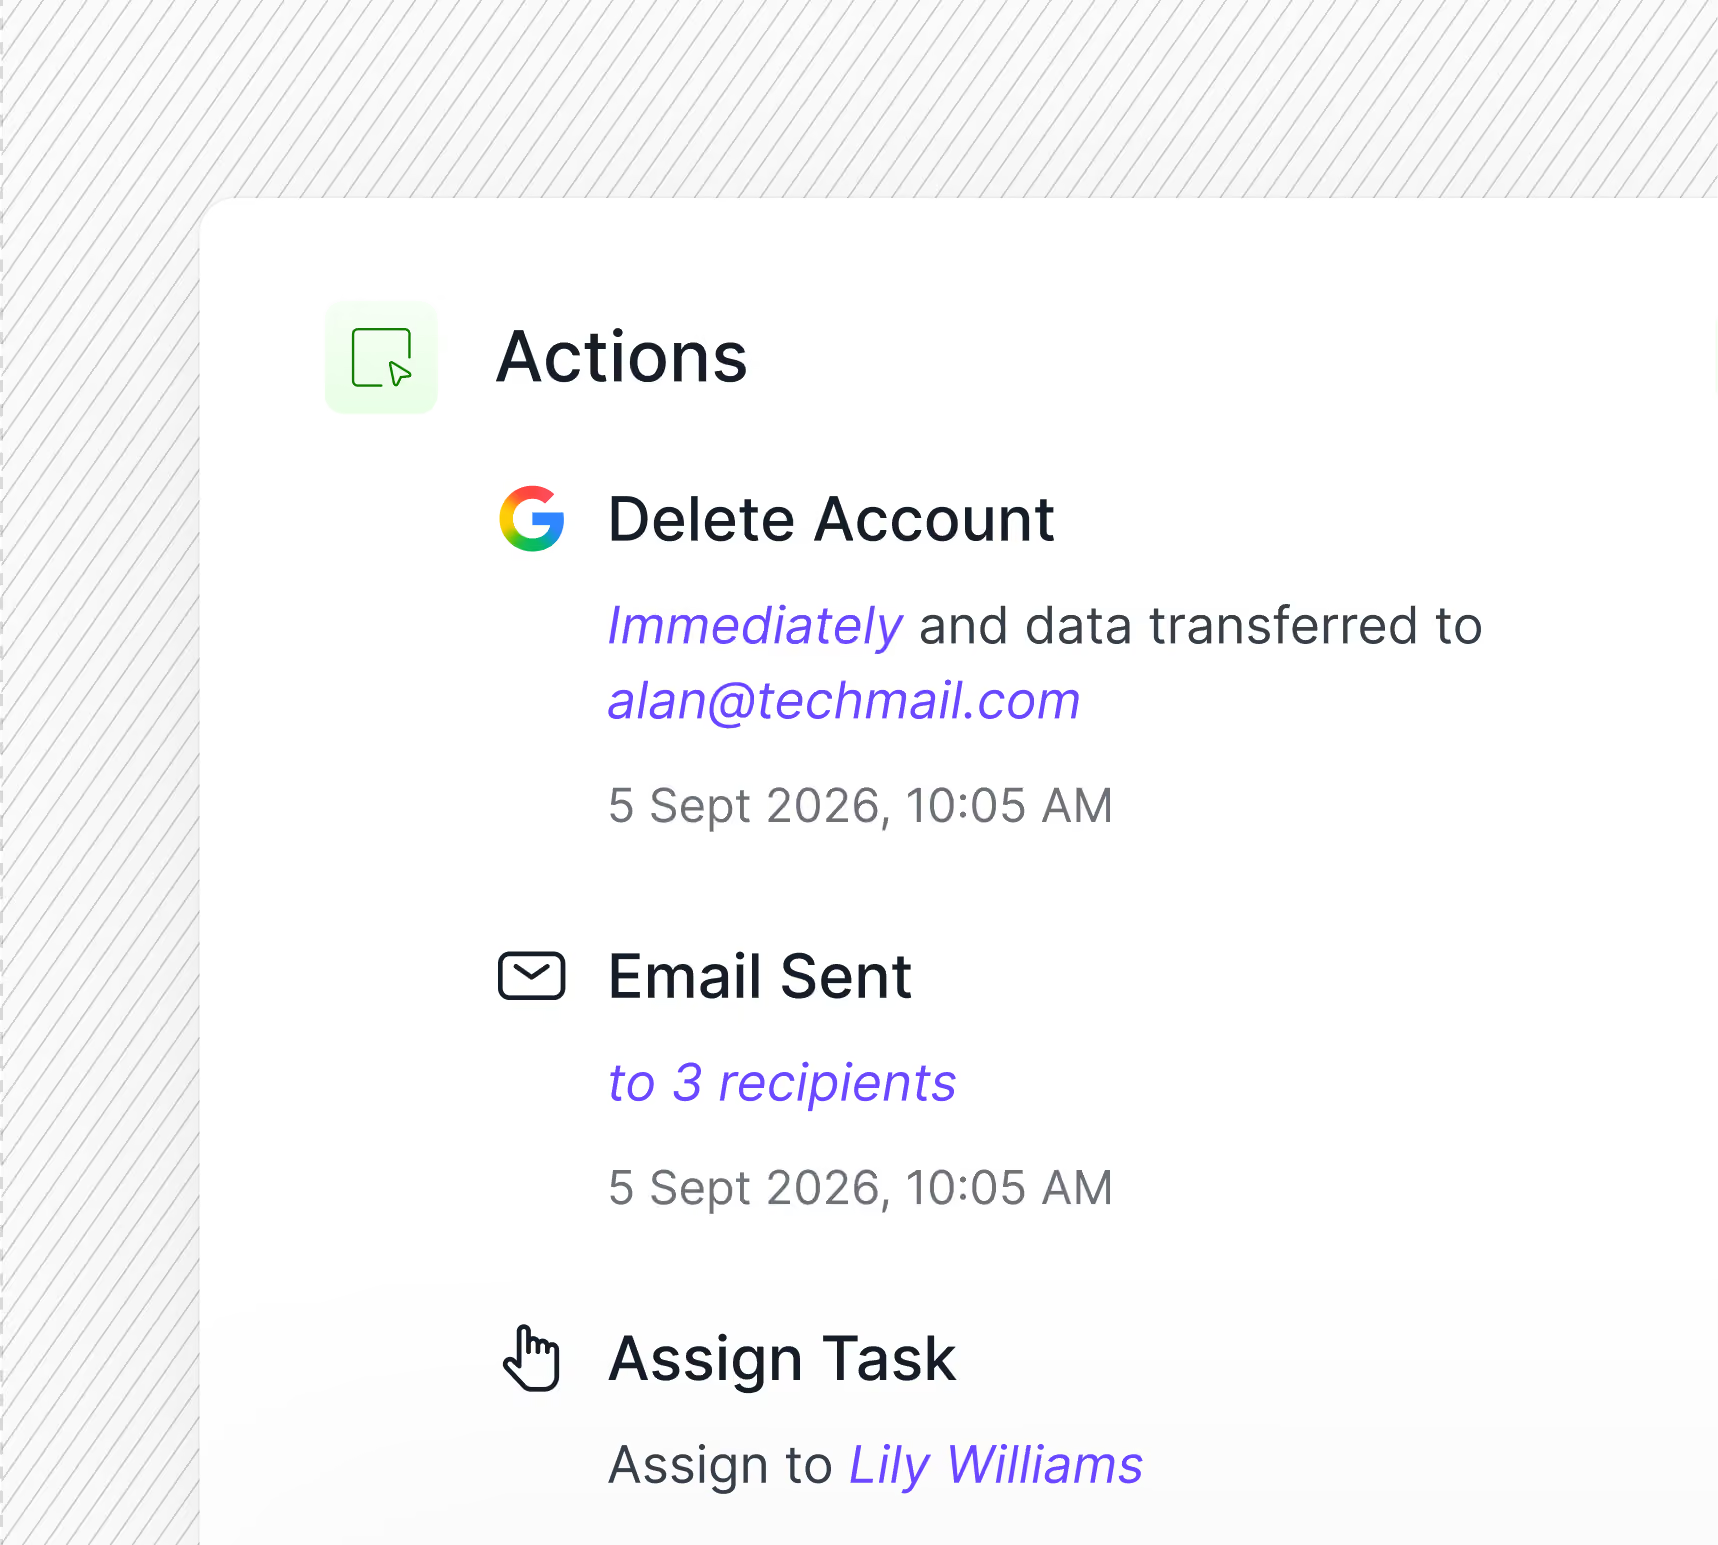
Set follow-up actions for approved and rejected requests, from adding the user to raising Jira tickets, and Josys triggers them automatically.
Every approval, rejection, and grant is logged,
so you're audit-ready by default.
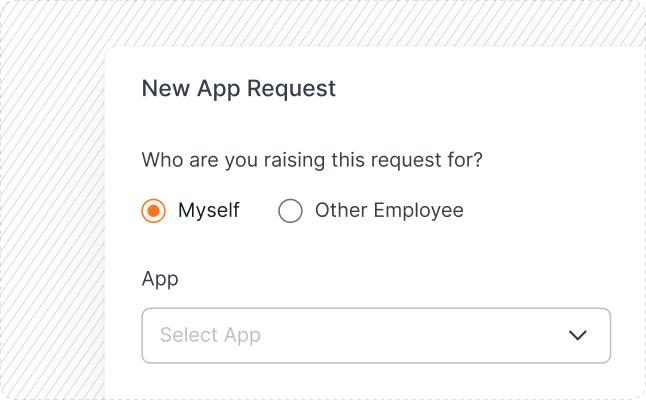
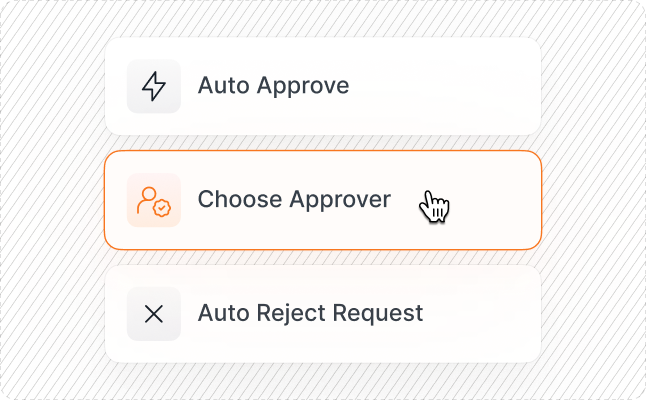
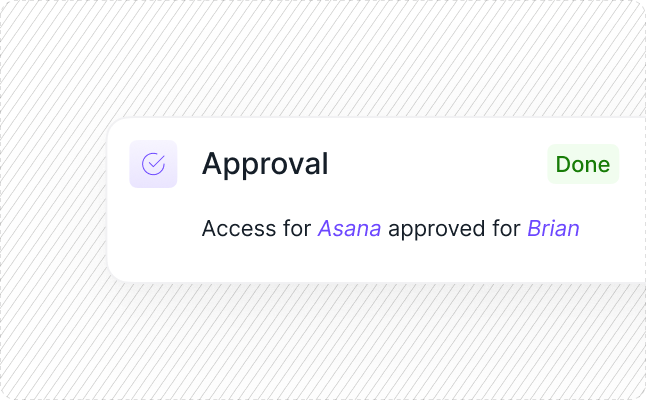

Make it easier for users to get access to the tools they need.


How Josys works



Key Features


Sign-up for a free Josys account to transform your IT operations.


End-to-End Identity
Governance made easy for IT


