

Detect leaked credentials
before attackers do
Josys continuously monitors stealer logs, dark web forums, and open web sources for leaked employee credentials - then triggers automated remediation workflows to contain the threat across every connected app.
Stolen credentials are the
fastest path into your SaaS stack
Credential leaks often surface on the dark web long before a breach is detected. But most teams still respond manually and too late. Josys connects credential threat intelligence directly to identity and access data, so exposed accounts are detected and remediated from one place.
From detection to remediation
without switching tools

Detect
When a compromised credential matches an employee, Josys surfaces the affected identity/device, leak source, and detection details, no manual triage required.

Map
The compromised identity auto-matches to the user's Josys profile, instantly showing their app access, permission levels, and managed/tracked status.

Respond
Trigger remediation workflows directly from the alert, with multiple response paths based on severity and your security posture.
across every connected app.
When a credential leak is detected, trigger Josys's off-boarding workflow to deactivate the affected user's accounts across every integrated application — in one action. No manual app-by-app cleanup required.
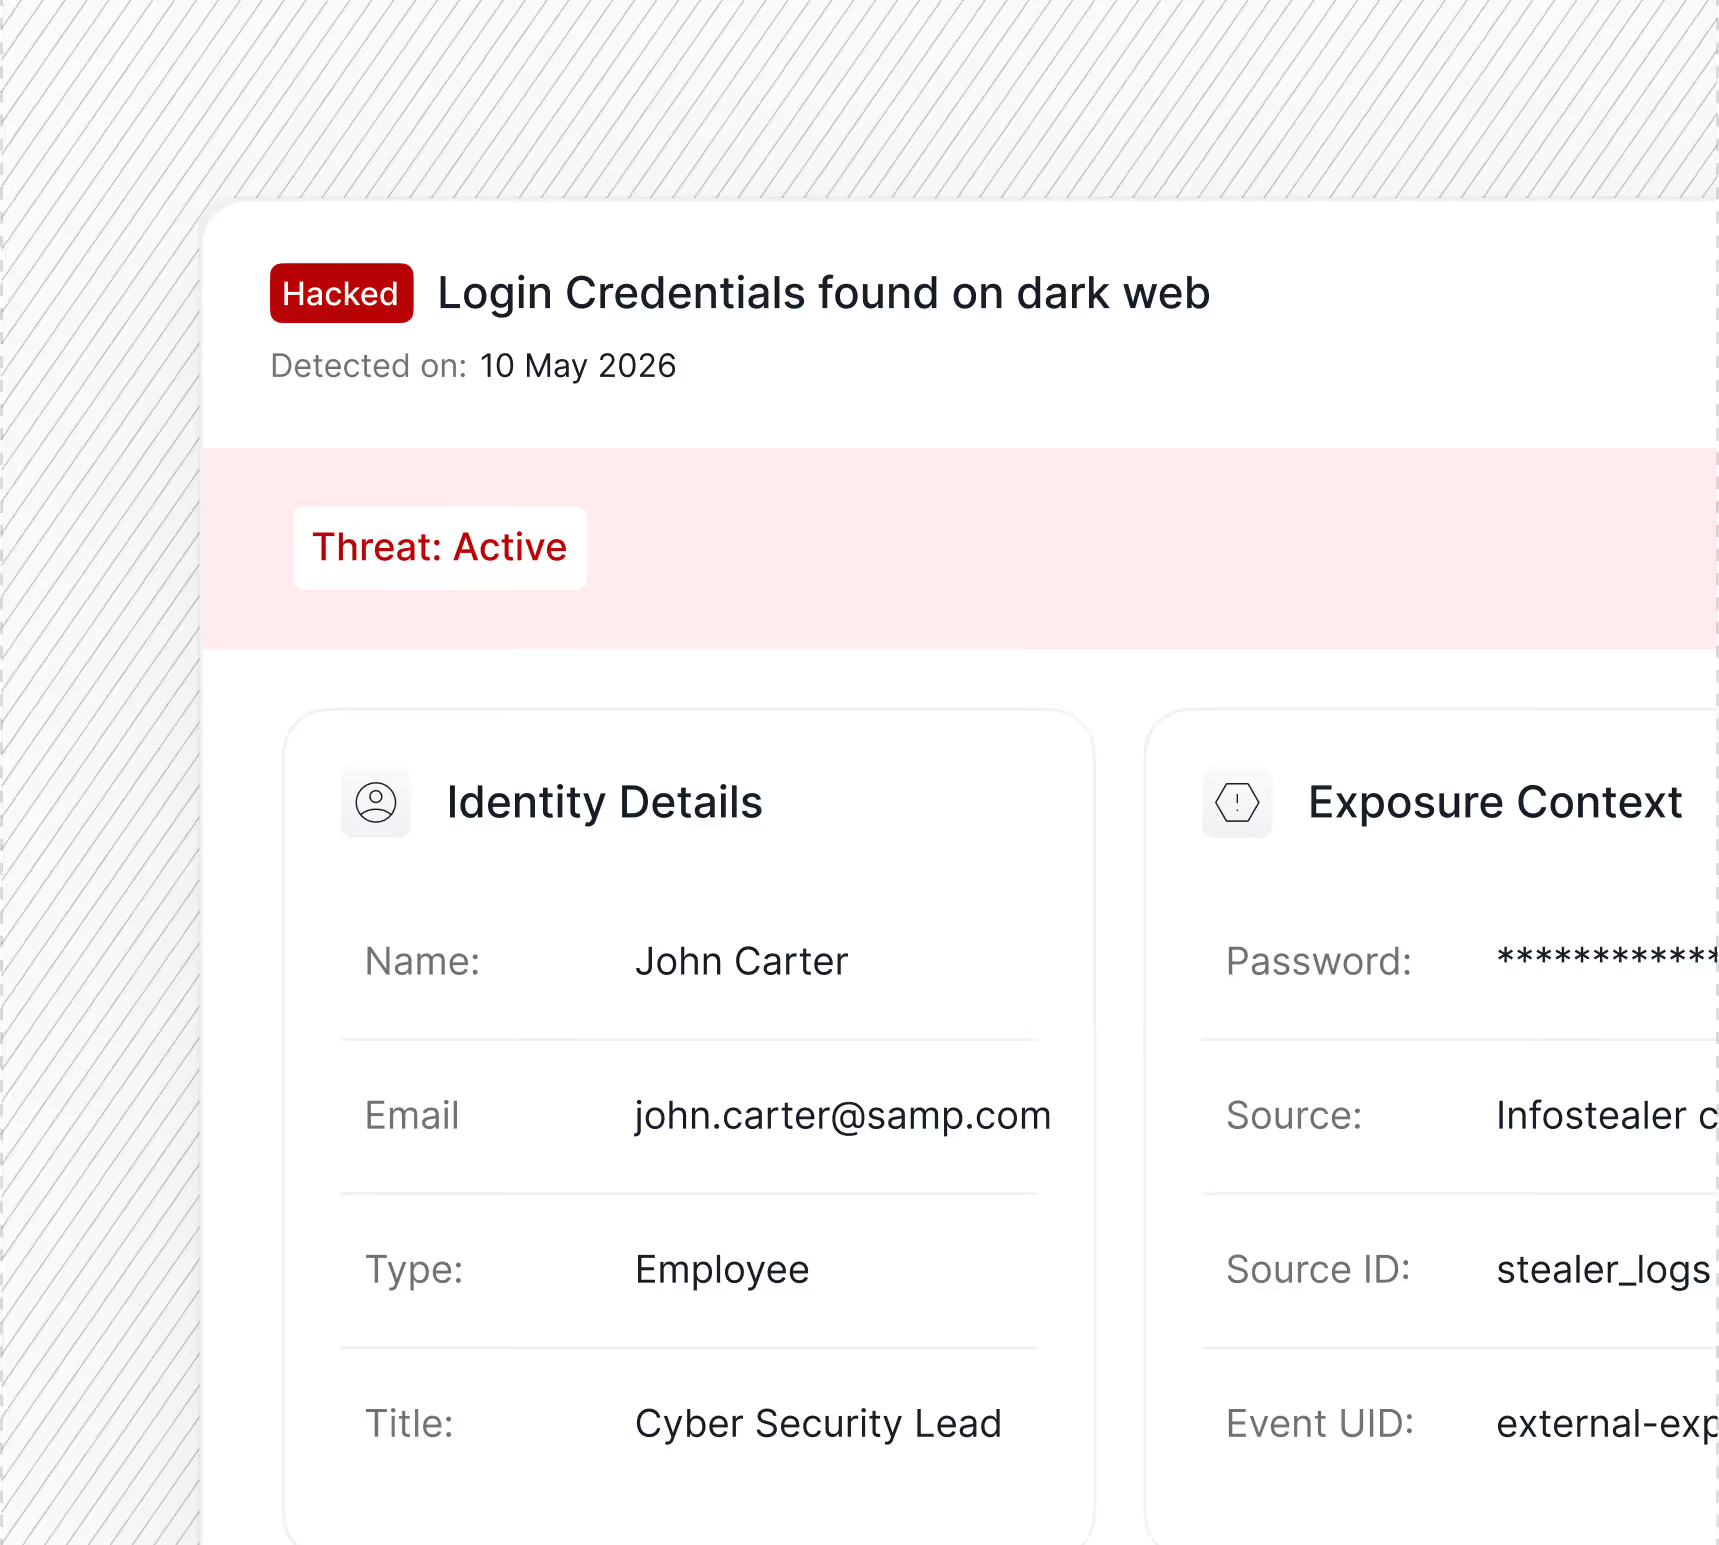
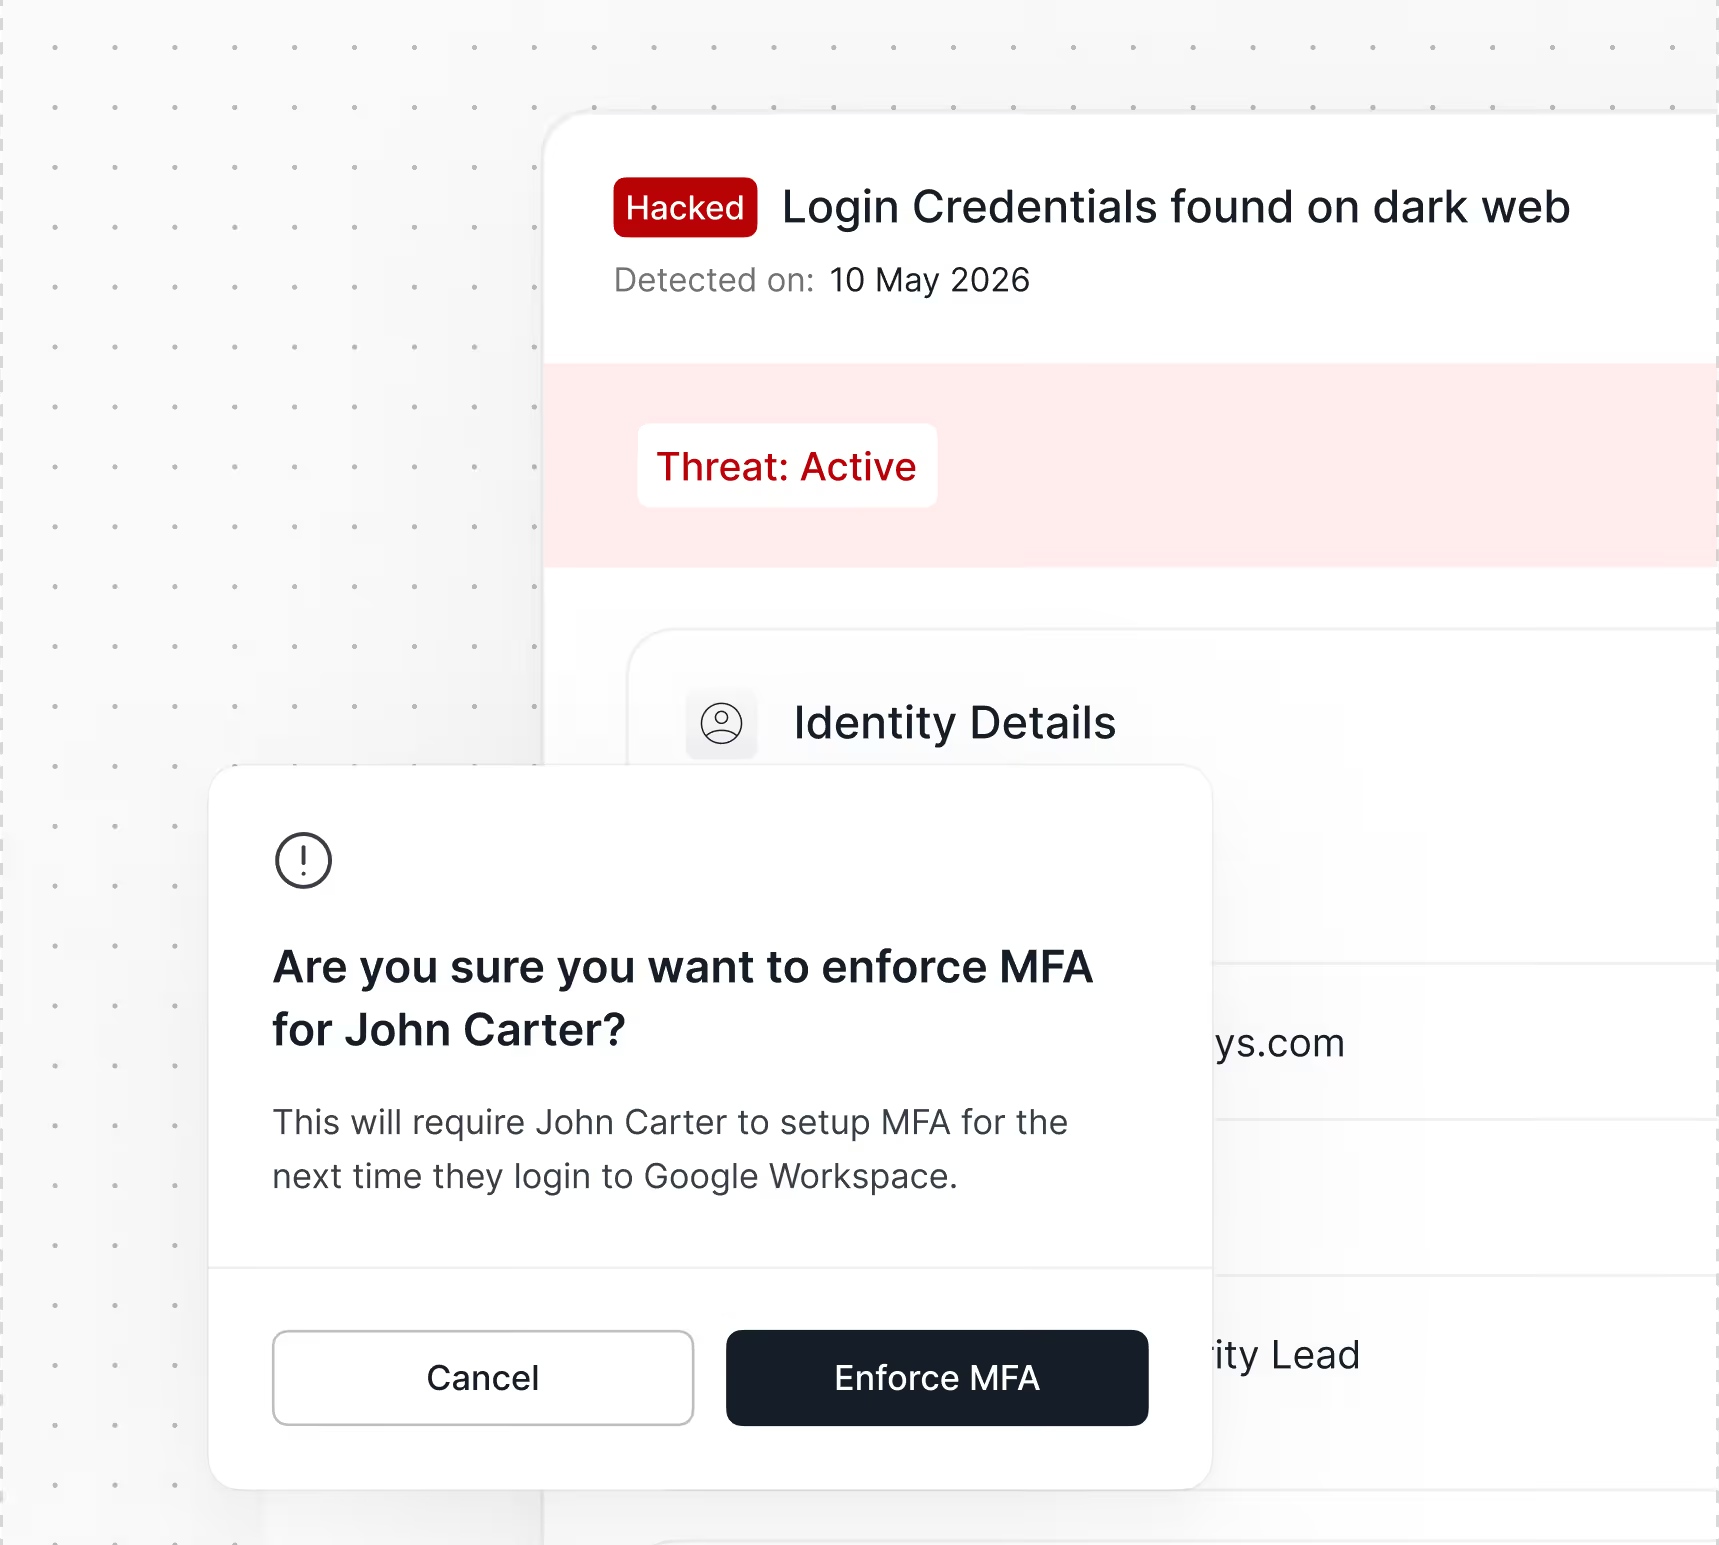
compromised identity
Instead of full deactivation, enforce multi-factor authentication on the affected user's Entra ID account directly from Josys. This secures the identity while keeping access intact for business continuity.
for controlled response
Route the remediation action through an approval step via Josys access review, so a security lead or IT admin can validate the response before it executes. Useful when you want a human in the loop before deactivating accounts.
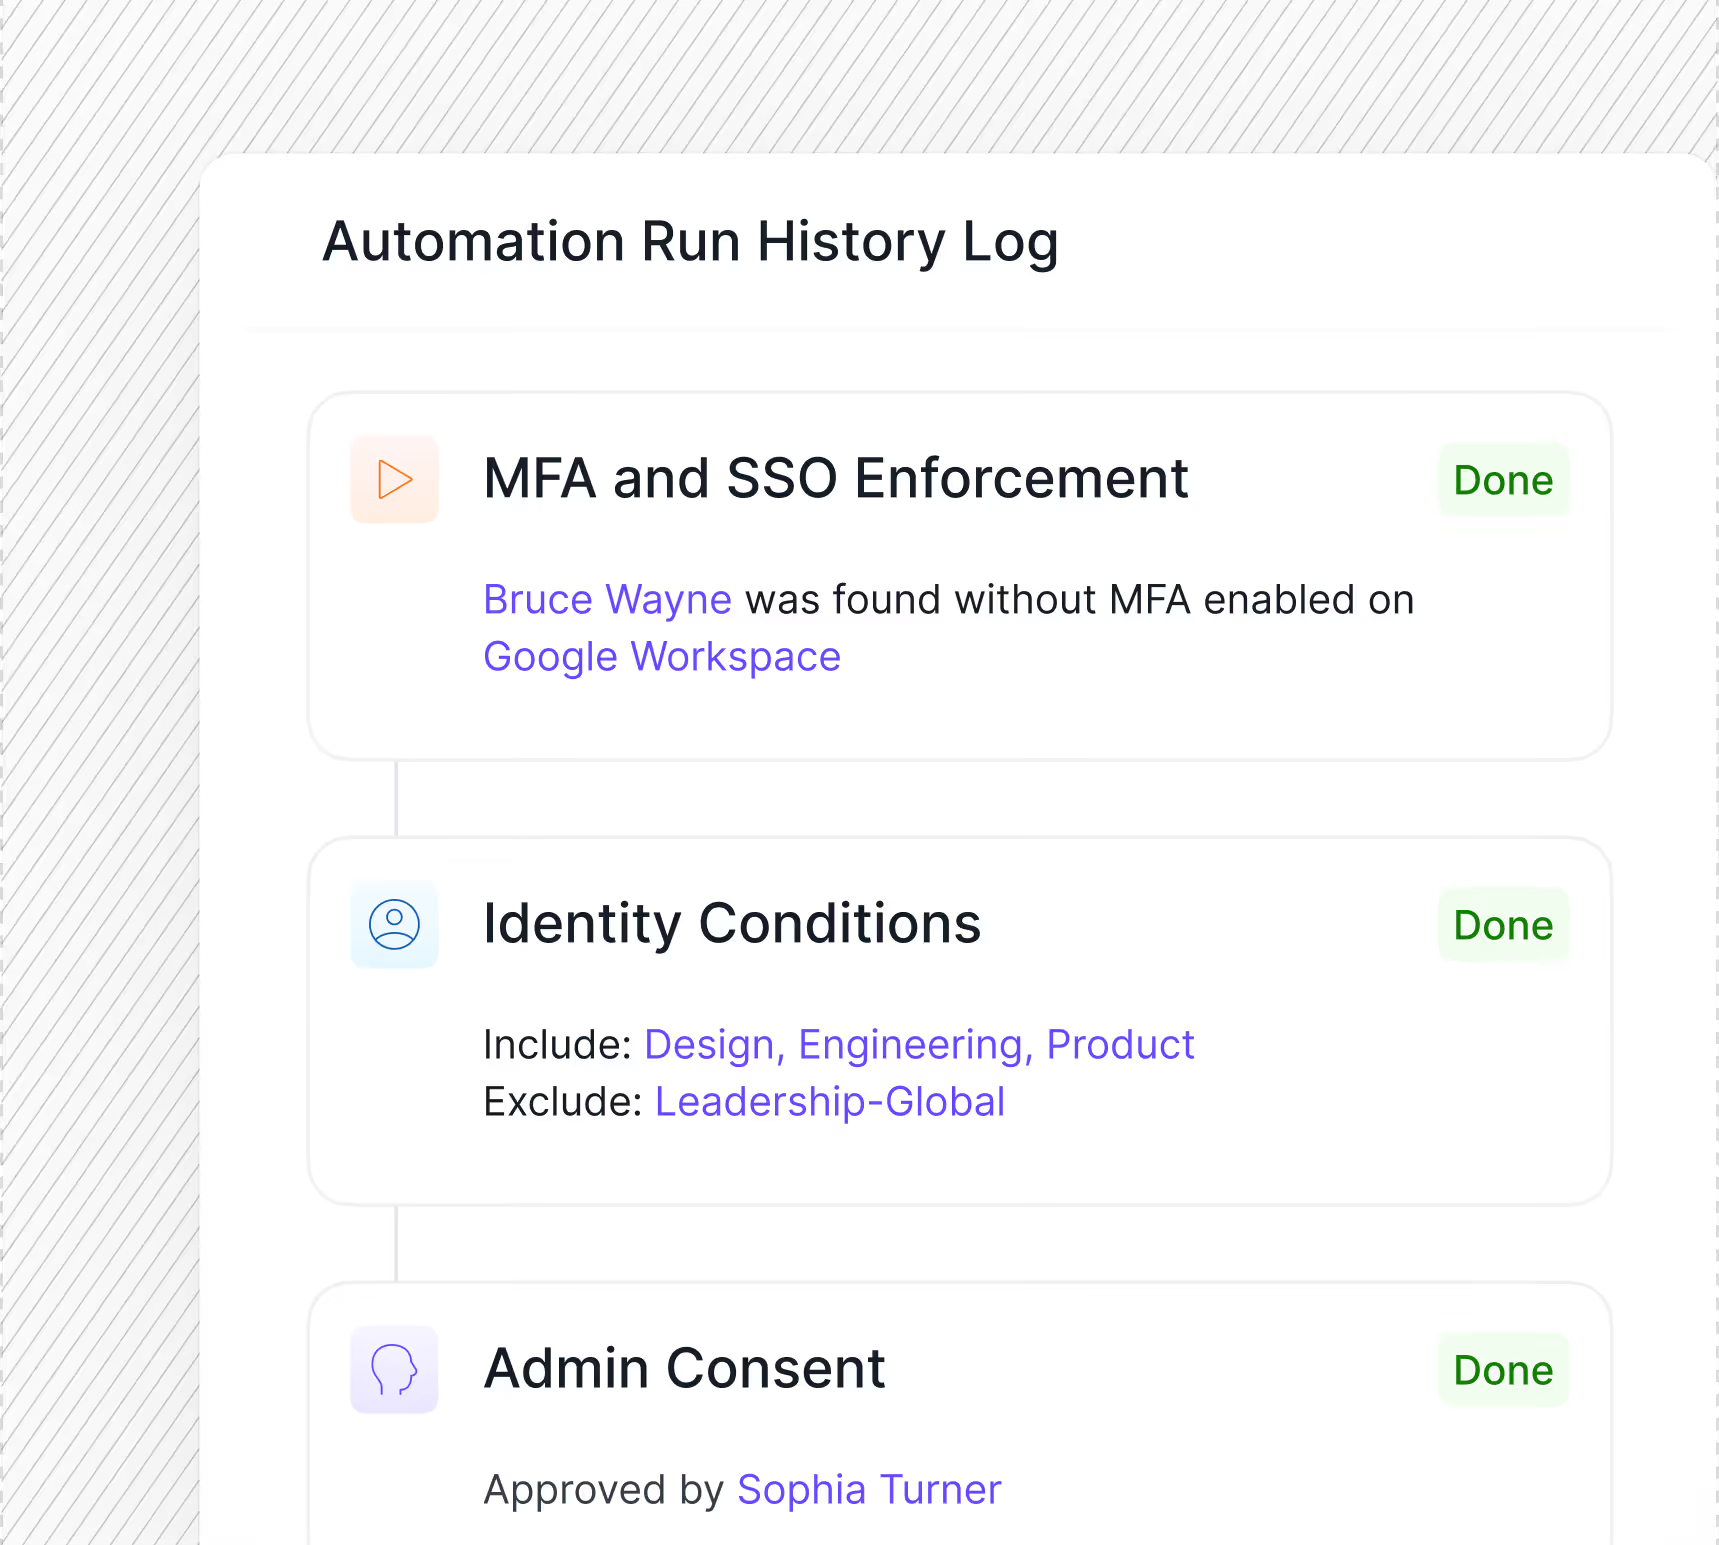
Continuous monitoring
across the sources that matter

Stealer logs
Credentials harvested by info-stealer malware and circulated across underground channels. Josys monitors these logs for matches against your organization's employee accounts.

Dark web forums
Leaked credential dumps, account lists, and access-for-sale postings on dark web marketplaces. Josys scans these sources continuously, not on a scheduled basis.

Open web & paste sites
Publicly exposed credentials posted on paste sites, code repositories, and open forums. Often the first sign that a broader breach has occurred.
Frequently Asked Questions

あなたの会社の
認証情報 は、
すでに漏れている
かもしれない。
認証情報の漏えいは、どれだけ対策しても防ぎきれない。
求められるのは、リアルタイム検知と即時アクション。
あなたの会社、大丈夫ですか?
漏えいしているID・パスワードを無料で調査
サイバー攻撃被害の原因は、1人の認証情報の漏れ
225社中217社で、過去3年間に情報漏えいを確認。
漏えい件数の合計は279,206件。従業員数に対する漏えい率は2.9%。
出典:ジョーシス株式会社「日経225企業におけるサイバーセキュリティに関する調査」(2026年6月11日発表)。対象:日経225構成企業225社及びそのグループ企業、期間:2023年3月1日〜2026年6月1日。
※数値はダークウェブ上などで当該企業の情報として流通している件数で、当該企業の情報でない可能性や、すでに無効化された情報を含む可能性があります。漏えい件数・漏えい率は異常値の1社を除く224社で集計。
認証情報の漏えいは、起きる前提で考える。
大切なのは、漏えいをリアルタイムで検知し、すぐにアクションすること。
漏えいは、
防ぎきれない。
フィッシング、端末のマルウェア感染、利用サービスからの流出。ID・パスワードの漏えいは、どれだけ対策しても起こりうるものです。
ダークウェブで
売買されている。
漏えいに気づかなければ、盗まれた認証情報は
不正アクセスの入口として使われ続けます。
リアルタイム検知と
即時対応
外部に漏れた認証情報をリアルタイムで検知し、担当者へ通知。被害が広がる前に、アクションできます。
 TEMSAMPLE/架空データ
漏えいしている認証情報の一覧
説明用の見本です。実際の診断結果ではありません。
漏えい対策は、検知だけでは完結しません。
検知した情報を整理し、是正まで実行してはじめて、リスクは低減します。
漏れていないか、わからない…
見極められない…
どこまで進んだか追えない…
 Josys TEMなら

自社に関わる漏えいを
継続的に検知
外部の漏えい情報から、
自社に関わる情報を継続的に確認。

出所と影響範囲を整理し
優先順位を明確に
出所や関連サービスを分析し、
対応の優先順位を整理。

通知から是正まで
実施状況をフォロー
検知結果と確認すべきポイントを担当者へ通知。推奨対応を提示し、実施状況のフォローまで支援。
※ 内容・頻度・通知タイミングはプランによって異なります。パスワード変更などの実際の操作は、お客様が実施します。
96%以上の企業で、認証情報の漏えいを経験※
あなたの会社、大丈夫ですか?
漏えいしているメールアドレスとパスワードを、アカウントごとに特定します。
※日経225構成企業225社のうち217社(2026年6月ジョーシス調べ)
即時アクションを可能とする
ポリシーによる運用自動化
漏えいの検知をトリガーに、レビュアーへの確認依頼から、セッションの無効化などのアクションまで。決めておいた流れで、すぐに動けます。
- 1STEP 1|検知漏えいをリアルタイムで検知認証情報の漏えいを検知し、アカウント・レベル・脅威タイプを一覧で確認。
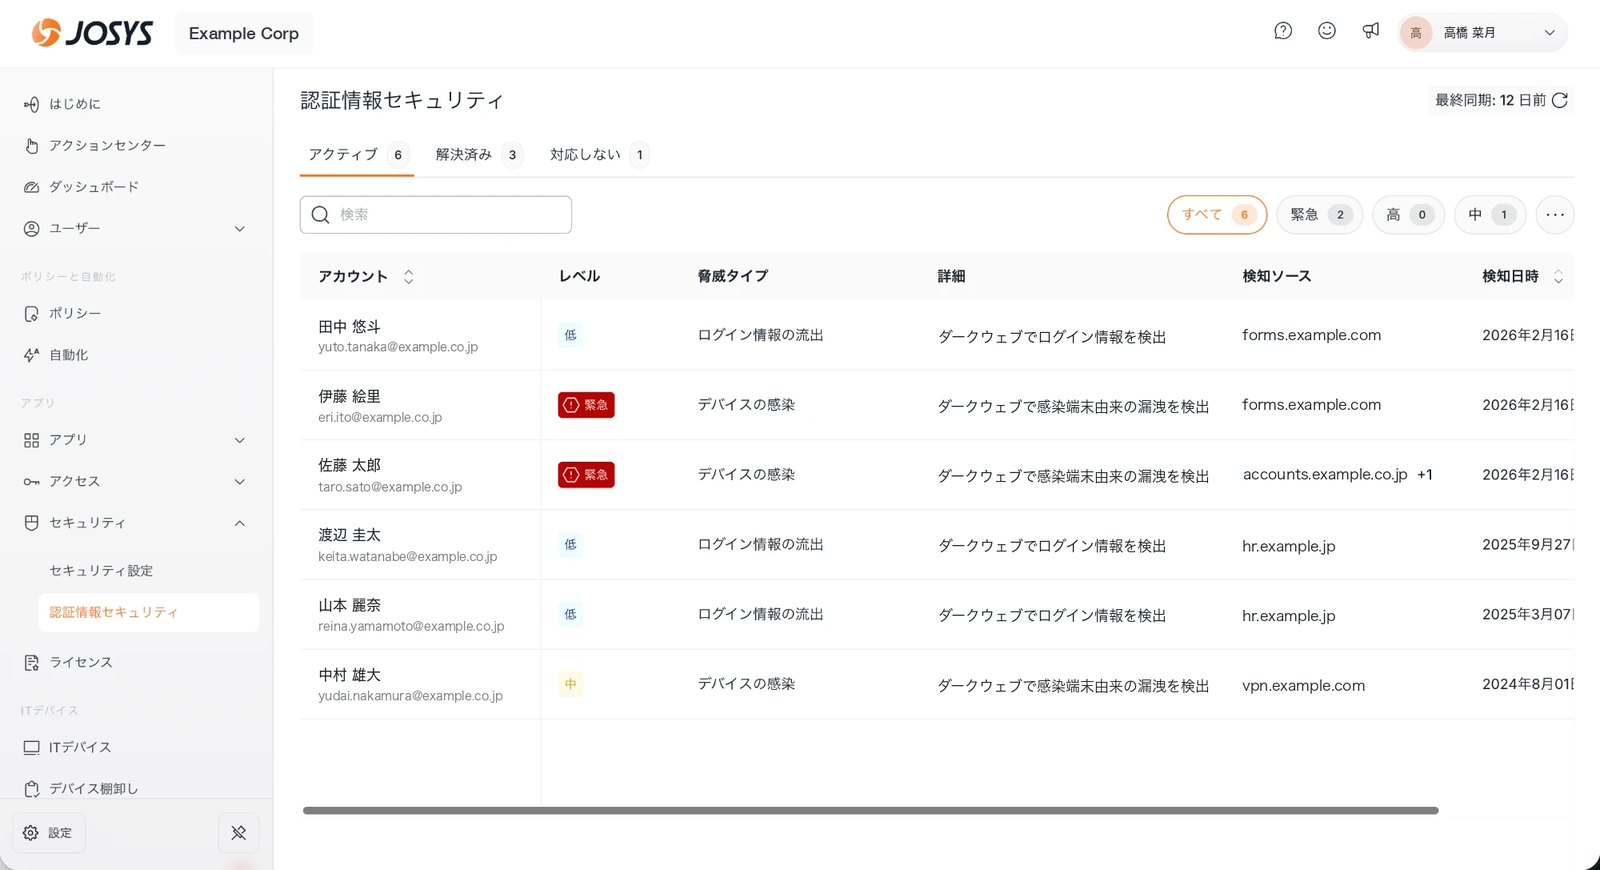
- 2STEP 2|トリガー検知をきっかけにポリシーが起動「新しい脅威が検出されたとき」をトリガーに、あらかじめ設定したポリシーを実行。
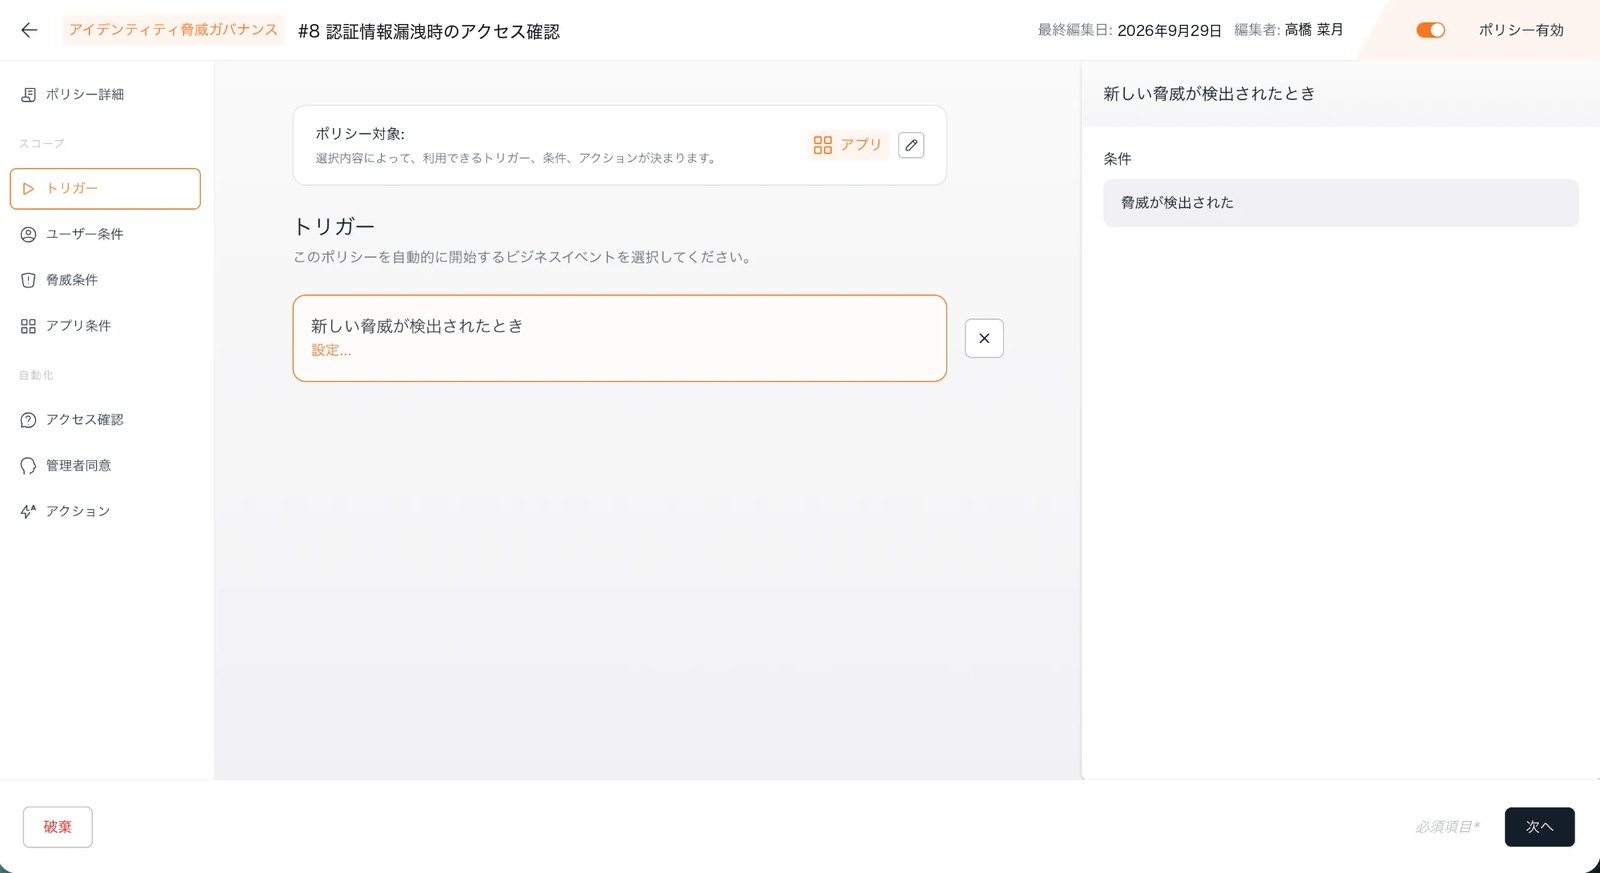
- 3STEP 3|レビュアーに通知指定したレビュアーへ確認を依頼脅威レビュアーに確認用の質問を送信。回答に基づいて次のアクションへ進みます。
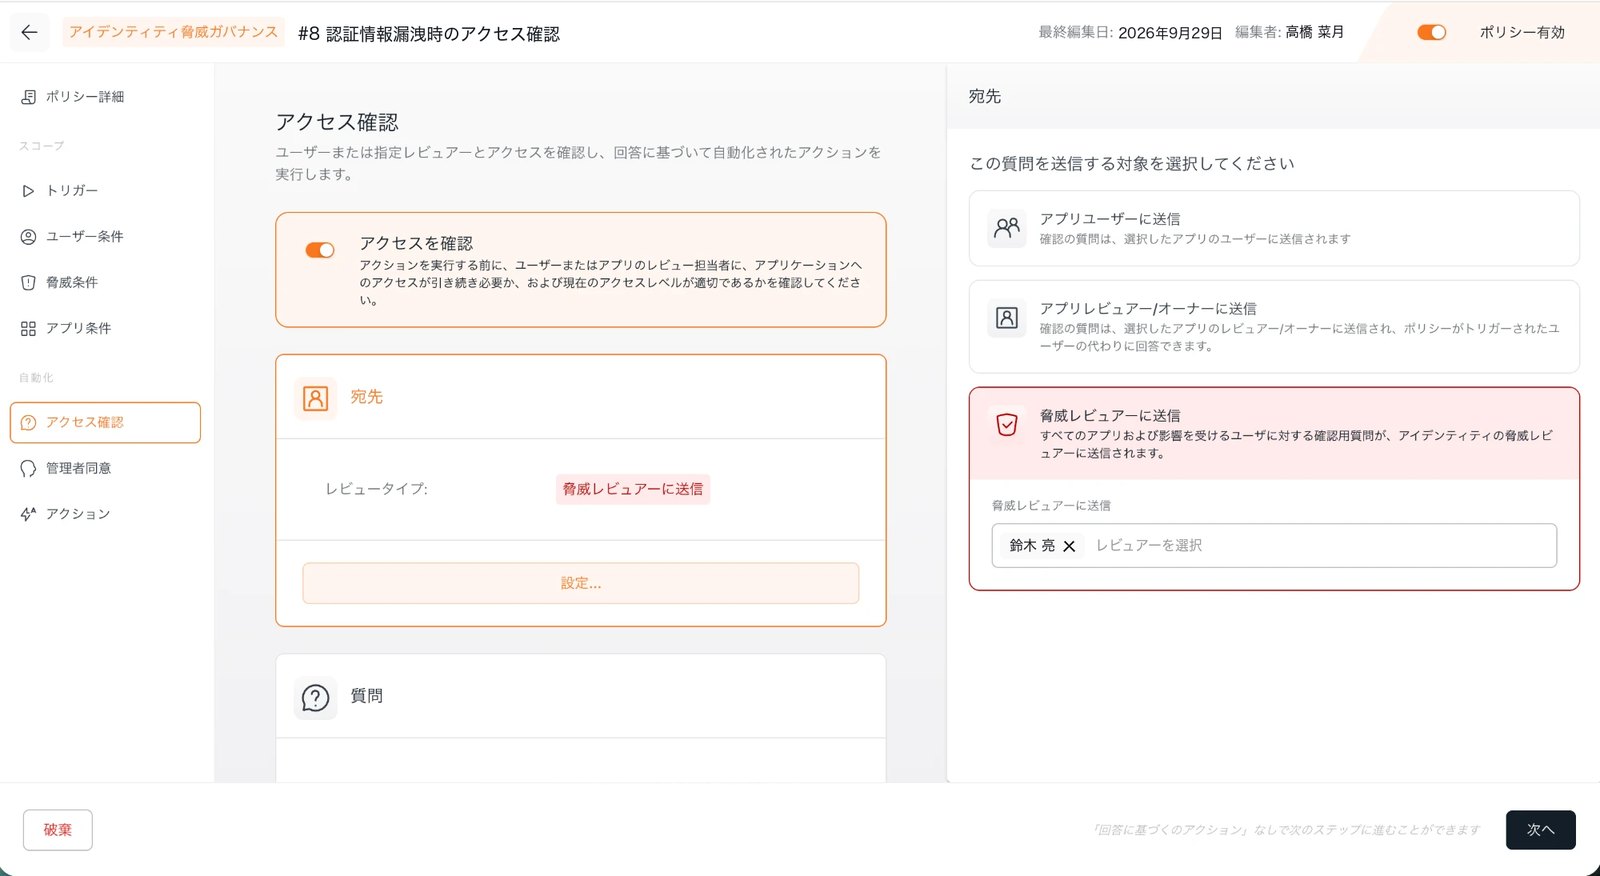
- 4STEP 4|アクションセッションの無効化などを実行推奨アクションに沿って、セッションの無効化やアカウントの対応を進めます。
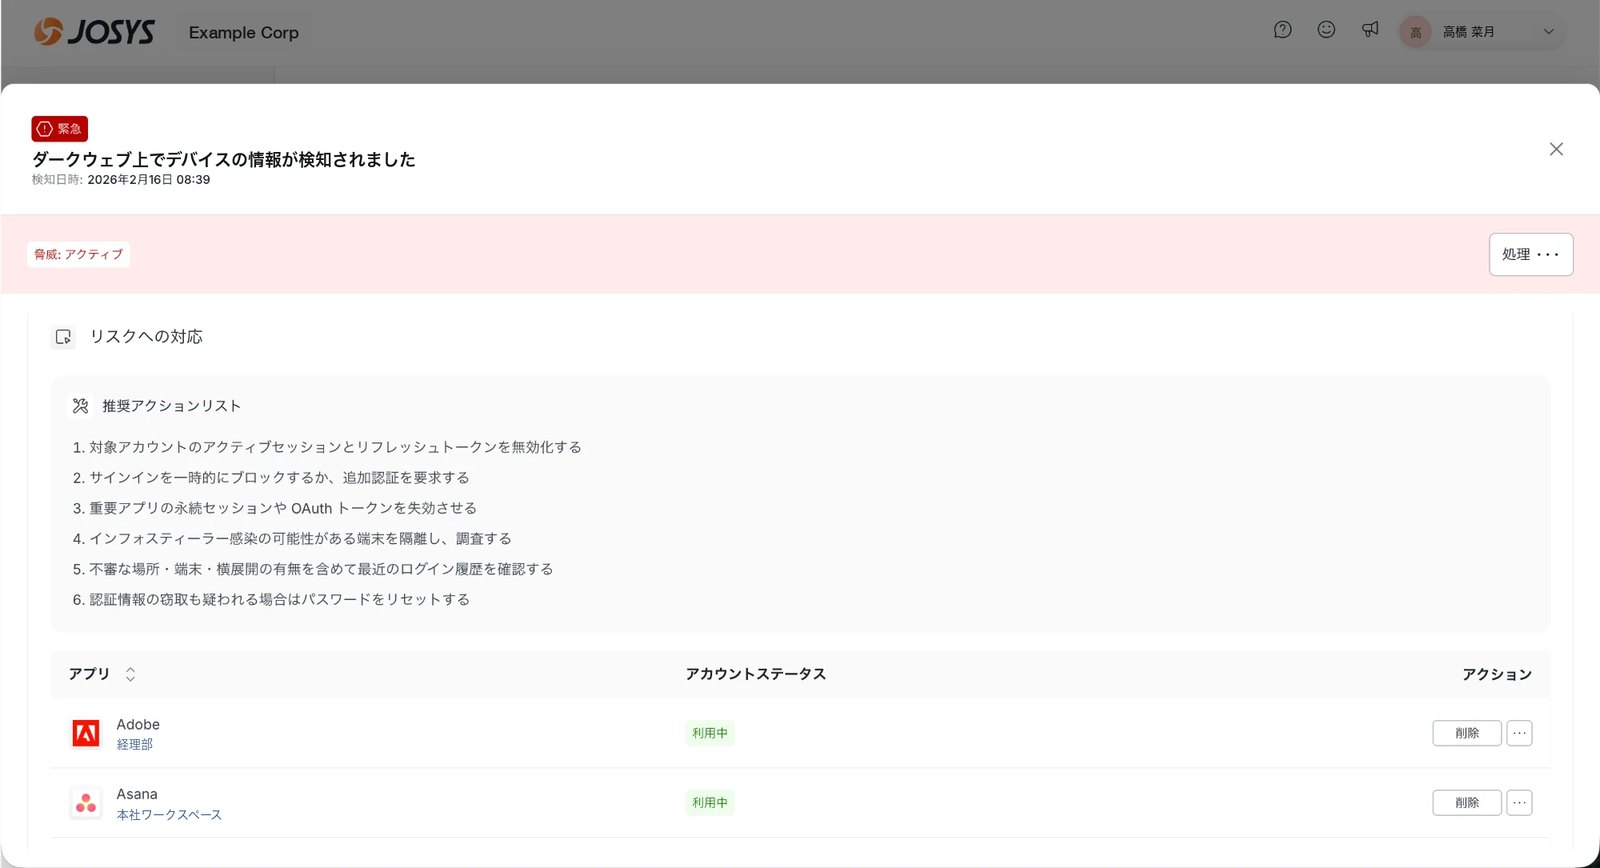
※画面はイメージです(表示している企業名・氏名・メールアドレスは架空のものです)。利用できるトリガー・通知先・アクションは、連携アプリや契約プランにより異なります。
メンバー・アプリ・デバイスの台帳がつながっているから、
影響範囲を正確に把握して、すぐに動ける。
漏えいした認証情報を、誰の・どのアプリの・どの端末に関わるものか、Josysの台帳上で突合します。
リアルタイムで検知
 統合台帳
すぐにアクション
- アカウントの停止
- 端末の隔離
- 本人・管理者への連絡
※ 概念図です。台帳との照合には対象情報の連携が必要です。支援範囲はプランによって異なり、実際の設定変更や無効化操作はお客様が行います。
まずは、自社の漏えい状況を確認しませんか?
漏えいしているメールアドレスとパスワードを、無償レポートでご確認いただけます。
Josys TEMが選ばれる、
3つの強み
広く見つけて、すぐに始めて、ずっと見張る。
250億件以上の漏えい情報から、
自社に関わるリスクを見つける。
250億件以上の漏えい情報データベースを対象に、自社ドメインに関連する情報を確認。
※250億件以上は漏えい情報データベースの収録件数です(自社の漏えい件数や検知実績ではありません)。取得可能なデータの範囲で調査し、すべての漏えいを検知することを保証するものではありません。
 Josys TEMが監視・照合
端末へのインストール不要。
自社ドメインだけで簡単調査。
外部の漏えいデータから、自社ドメインに関連する情報を確認します。
社内の端末へのインストール等の対応は必要ございません。
※外部の漏えいデータを調査するもので、社内の端末を直接スキャンするものではありません。
年1回の診断で終わらせない。
新たな漏えいを、継続的に確認。
一度きりの調査や年1回の診断では、そのあいだに起きた漏えいに気づけません。Josys TEMでは外部の漏えい情報を継続的に監視します。
※継続サービスの内容・範囲・通知タイミングは契約プランにより異なります。
無料調査とは別のお申し込み・ご契約が必要です。
※検知・通知の範囲は、取得可能なデータや契約プランにより異なります。すべての漏えいを検知することを保証するものではありません。
自社の認証情報が
漏れていないか
まずは確認しませんか?
自社ドメインに関連する外部の漏えい情報を調査し、確認できた内容を初期診断レポートでご案内します。
- 自社ドメインに関連する漏えいしたID・パスワードを検出
- 検出情報に含まれる関連サービス
- 検出内容の分類とリスクの内訳
お申し込み → 対象の確認・調査 → 結果のご案内
※取得可能な外部データの範囲で調査します。検出がない場合も、漏えいやリスクがないことを保証するものではありません。結果のご案内方法・日程は担当者からお知らせします。
TEMSAMPLE/架空データINITIAL ASSESSMENT REPORT
認証情報漏えい 初期診断レポート
検出内容の内訳
検出情報(一部)
よくある質問
無料調査は調査時点の状況をレポートでご案内します。継続サービスでは、契約プランに応じた継続確認や通知、対応対象の把握を支援します。
外部の漏えいデータから対象ドメインに関連する情報を確認する調査です。端末を直接スキャンするものではありません。
関連する端末に感染が残っている場合、変更後の情報も再び盗まれるおそれがあります。認証情報の変更に加え、端末やログイン状況などの確認も必要です。
調査対象のデータに含まれていない情報や、まだ確認できていない漏えいもあります。検出がないことは、安全を保証するものではありません。

End-to-End Identity
Governance made easy for IT


